> For the complete documentation index, see [llms.txt](https://docs.balena.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.balena.io/learn/accounts/fleet-members.md).
# Fleet members
BalenaCloud offers the ability to collaborate with other users on the platform by inviting members to your fleets, apps or blocks and assigning them a varying degree of access as per your requirement using Member types. To invite members to your organization, refer to [organization management](/learn/accounts/organizations.md#granting-access-to-fleets).
When a fleet needs to be shared with more than one user, the fleet owner can add new members. With paid accounts, it's possible to assign a level of access for a new member, based on the following types:
### Member types
#### Administrator
A new fleet in balenaCloud can only be created by an [administrator](/learn/accounts/organizations.md#managing-roles-and-access-in-an-organization) of an organization. Administrators are the only users who can add other fleet members or delete the fleet. Learn more about the [administrator role](/learn/accounts/organizations.md#managing-roles-and-access-in-an-organization) in an organization. 
#### Observer
Observers are given read-only access to the fleet and its devices. They are not able to modify, add, or remove any devices, nor are they able to perform device actions. This role can only be assigned by fleet owners on paid plans.
#### Operator
Operators have all the access given to observers, plus the ability to manage a fleet's devices. This means operators can add and remove devices, generate & revoke provisioning API keys, perform device actions, and modify device tags, metadata, and environment variables. Operators also have full [SSH access](/learn/manage/ssh-access.md) to the fleet's devices. This role can only be assigned by fleet owners on paid plans.
#### Developer
Developers are given, in addition to the access provided to operators, the ability to manage fleet software. This includes creating new releases, modifying fleet variables, and downloading balenaOS images. This role is the closest to a fleet owner—developers can do everything owners can except for deleting the fleet or adding new members. The Developer role can be assigned by fleet owners on free or paid accounts.
### Add a fleet member
To add a new member to your fleet, click on the *Members* tab of the fleet:
This brings up a list of all fleet members, if any have been assigned. Click on the *Add member* button in the top left:
The *Add member* dialog has a dropdown with descriptions of the member types, as well as information about which types are available based on your billing plan. Choose a level of access, then enter the email address of the new member:
{% hint style="warning" %}
Fleet members must have already signed up for a balena account before they can be added to a fleet.
{% endhint %}
After you click *Add*, you will see the new member in the "Pending invitations" list. From here, you can edit access levels or remove the user if necessary.
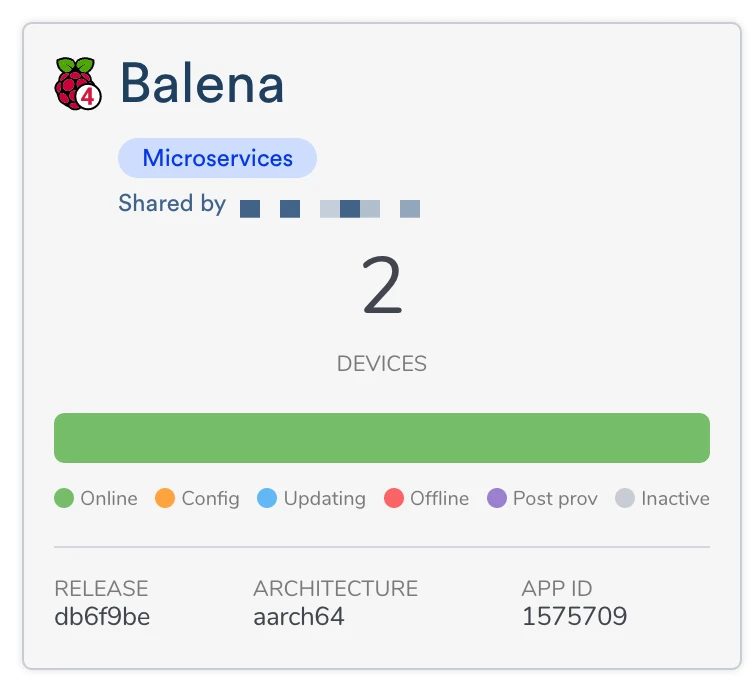
All users that have been added to a fleet will see that fleet in their dashboard, with an indicator to designate it has been shared by the fleet owner:
Fleet members will have the option to remove themselves from a fleet by clicking on the members tab, selecting the checkbox by their name from the member list, clicking on the *Modify* button, and selecting *Delete member*.
{% hint style="danger" %}
If you remove your member access to a fleet, you will not be able to undo the action. Only the fleet owner will be able to restore your access.
{% endhint %}
### Custom roles for fleets
You can create more granular permissions for fleet or block members by creating a custom role. These custom roles are managed at the organization level and assigned to members via the members tab of a fleet or a block.
{% hint style="warning" %}
This feature is only available on [Prototype, Pilot, and Production plans](https://balena.io/pricing/).
{% endhint %}
#### Creating a custom role
You can add, view, and delete custom roles from the "Fleet roles" tab under an organization.
Click on the "Add new custom role" button under the "Custom Roles" section of the page. After you provide a name and description for your new custom role, you'll have the option to use an existing role as a template for your new role. This is the recommended method though you can also elect to start from scratch.
You can select which permissions the role will have from among a long list. Simply click the switch next to the desired permission to enable or disable it. When you are finished, click the "Review" button at the bottom of the page. At that point you will see all the properties of your new custom role. You can either go back and make changes, or click "Add new role" to finalize the role. You can always go back later and make changes.
#### Editing custom fleet role permissions
To edit the permissions of an existing custom role, click on your role in the "Custom Roles" list from the organizations "Fleet roles" tab. That will load a summary of your custom role. In the "Permissions" section of the page, click on "Manage permissions" to edit the permissions for the selected role.
#### Editing or deleting a custom fleet role
When you click on a role listed in the "Custom Roles" section of the "Fleet roles" it loads the role summary page. In addition to editing the role permissions as described above, you can also edit the role name and description. This is accomplished by hovering your pointer over the name or description to reveal a pencil icon. Clicking on this icon will allow you to edit the selected field.
At the bottom of this section is the "Delete role" button. When you delete a custom role, any members or teams that were assigned to the deleted role will be removed from fleets that utilized that role.
#### Assigning a custom fleet role to a member or team
Once you have created a fleet role, you can assign it to members of a fleet. Select your fleet and then click the "Members" menu item.
On the members page, to assign a custom role to an existing member, select the check box next to the member's name and then click the "Modify" dropdown. From the dropdown menu, select "Edit access".
Once you select "edit access" an "Edit access" popup form will allow you to select the role you want to assign to the member, including any custom fleet roles you have added to the organization. Note that you may need to scroll down the list to see the available custom roles.
To assign roles to a new member not already a part of the fleet, click the "Add member" button. The "Invite fleet member" popup will be displayed where you can enter the email address of the invitee as well as select a custom role from the radio buttons.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.balena.io/learn/accounts/fleet-members.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.